Perimeter Defense Is Not Information Security
Traditional security models assume a trusted interior and defended boundary. Modern threats operate inside that boundary.
Assumed-Trust Architecture
Systems built before Zero Trust treat interior traffic as safe.
Compliance as Checkbox
Security certifications satisfied on paper but not enforced architecturally.
Supply Chain Opacity
Components from untrusted sources embedded in critical systems.
Detection Gaps Between Assessments
Point-in-time reviews leave months of unmonitored operation.
From architecture to continuous hardening.
Security Architecture
Security Architecture
Design layered Zero Trust controls for every system boundary.
Zero Trust Implementation
Zero Trust Implementation
Implement identity verification and micro-segmentation at every boundary in the system.
Supply Chain Verification
Supply Chain Verification
Verify the provenance of every component before it becomes part of the system.
Continuous Monitoring
Continuous Monitoring
Deploy real-time detection so gaps are found immediately, not at the next scheduled review.
Ongoing Hardening
Ongoing Hardening
Harden the system continuously against new threats as they emerge, not on a fixed cycle.

Zero Trust Architecture
Micro-segmentation and identity verification at every boundary.

Identity & Access Management
Authenticate and authorize every access request, every time.

Continuous Security Monitoring
Real-time detection, not periodic assessment.

Supply Chain Risk Management
Verify provenance of every component in the system.

cATO Implementation
Continuous authorization through automated security controls.

Adversarial Testing & Red Team
Validate defenses against real-world attack techniques.
Layered security
Security at every layer.
Zero Trust architecture showing micro-segmentation, identity verification at each boundary, continuous monitoring — versus traditional perimeter-only defense.
Why Agencies Choose DTSI
Zero Trust from the foundation. Adversary-tested. cATO-ready.
Zero Trust from the Foundation
Security is architectural, not appended after construction.
Adversary-Tested
Red team and offensive simulation validate defenses against real tactics.
cATO-Ready
Continuous Authorization to Operate through automated controls.
Customers + Partners
Trusted in IT & Cyber Expertise for 44 Years. We enable the DoD and all branches of service to maintain peak readiness and deliver mission results through proven technical expertise, operational support, and cybersecurity strength.
ARCADIS
City of San Antonio
State of Florida
State of New Jersey
Nantucket
United States Air Force
Copper River
Lockheed Martin
Booz Allen Hamilton
Abacus Technologies
Leidos
Northrop Grumman
ARCADIS
City of San Antonio
State of Florida
State of New Jersey
Nantucket
United States Air Force
Copper River
Lockheed Martin
Booz Allen Hamilton
Abacus Technologies
Leidos
Northrop Grumman
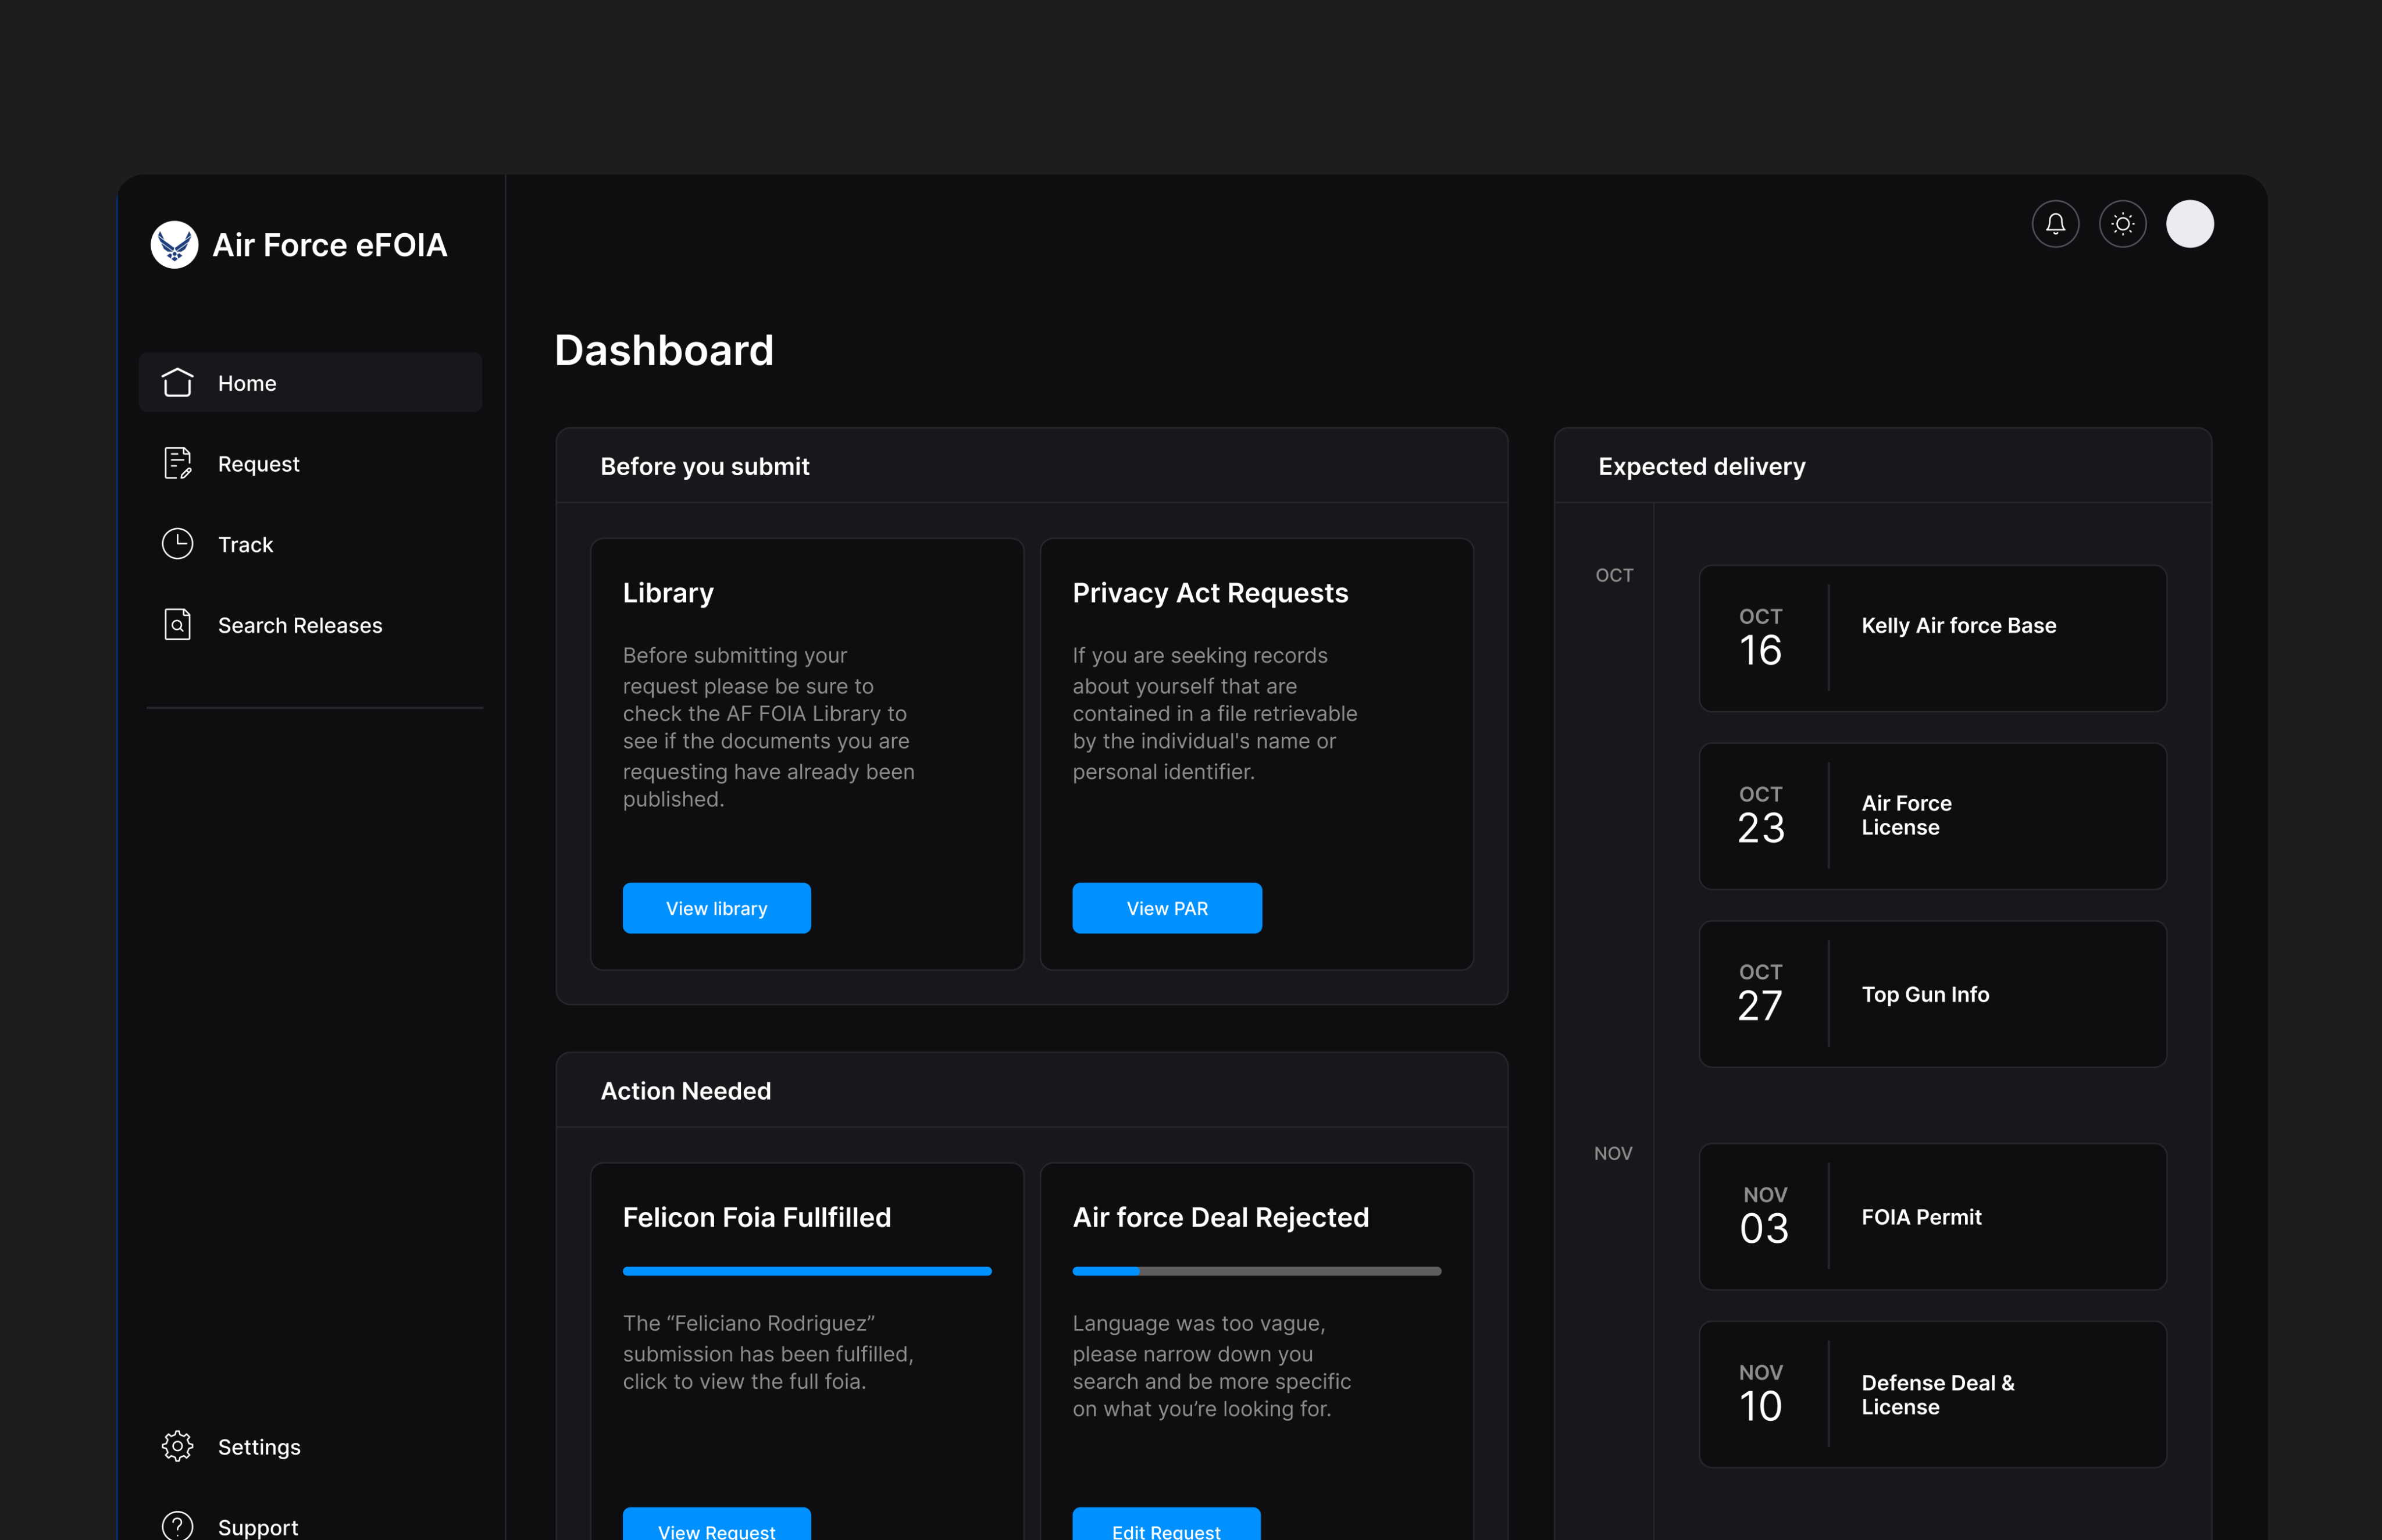
Book Your Personalized Demo
Discuss your information security requirements with DTSI.
In your demo, we'll cover:
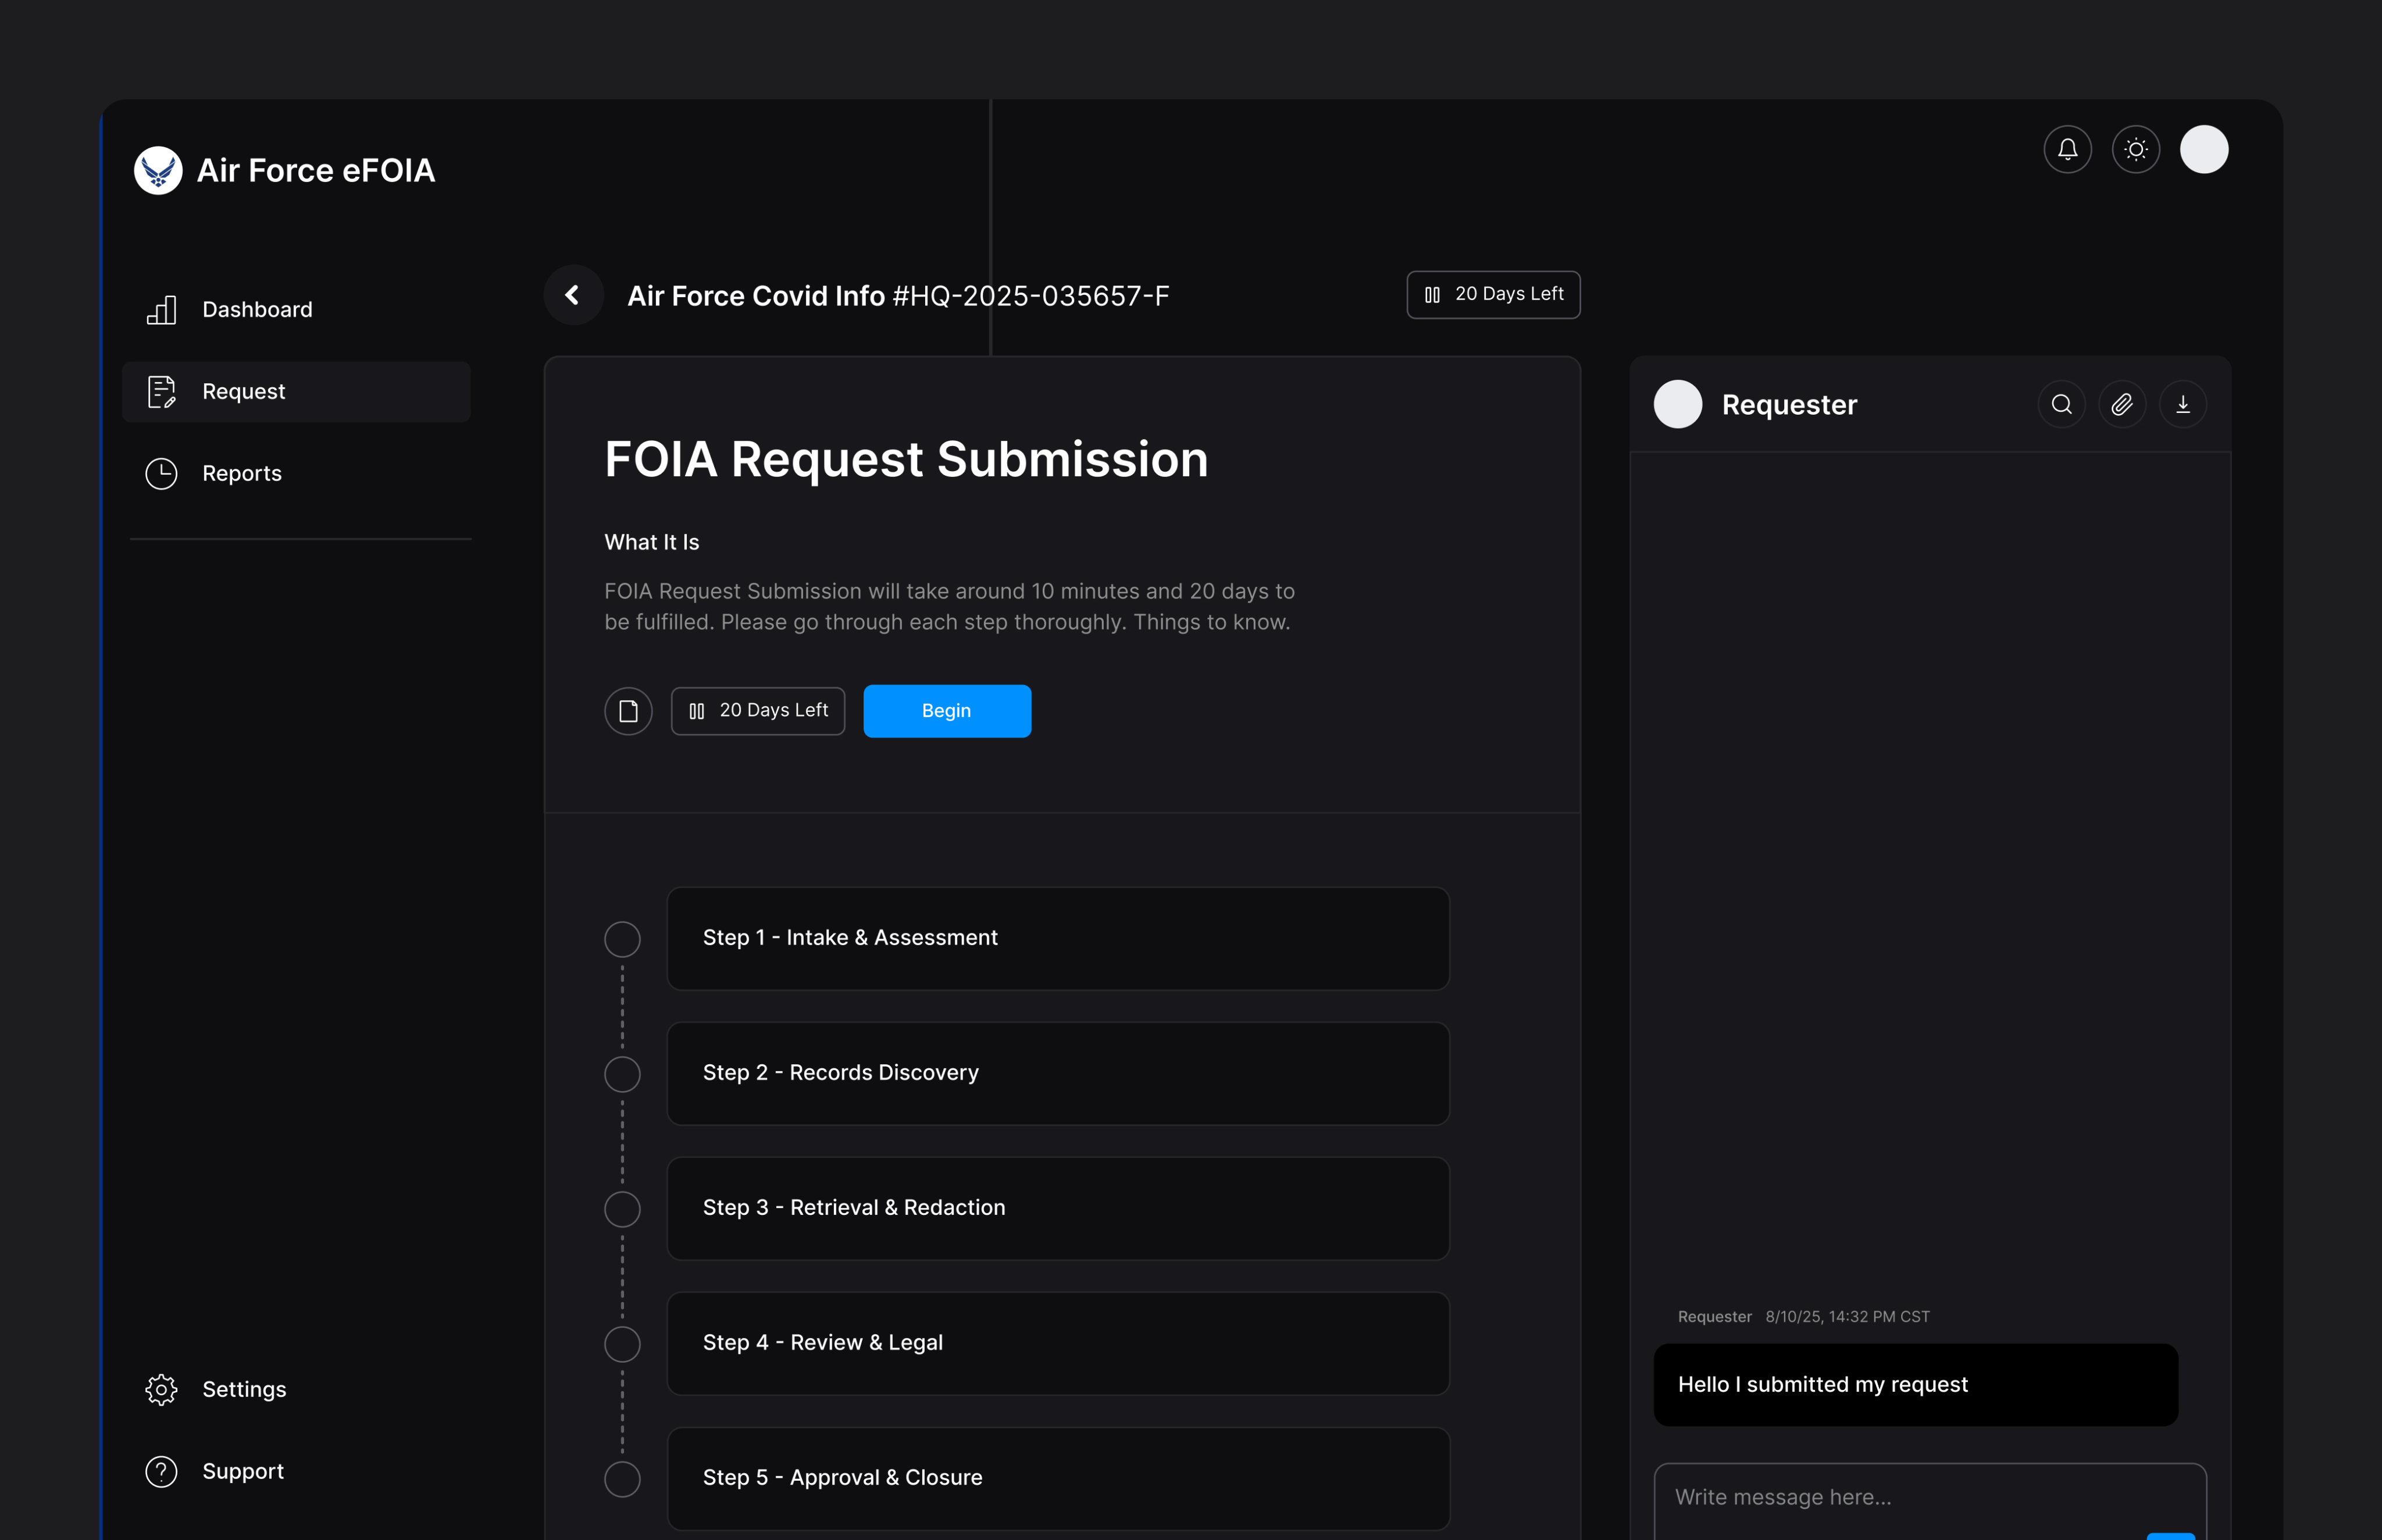
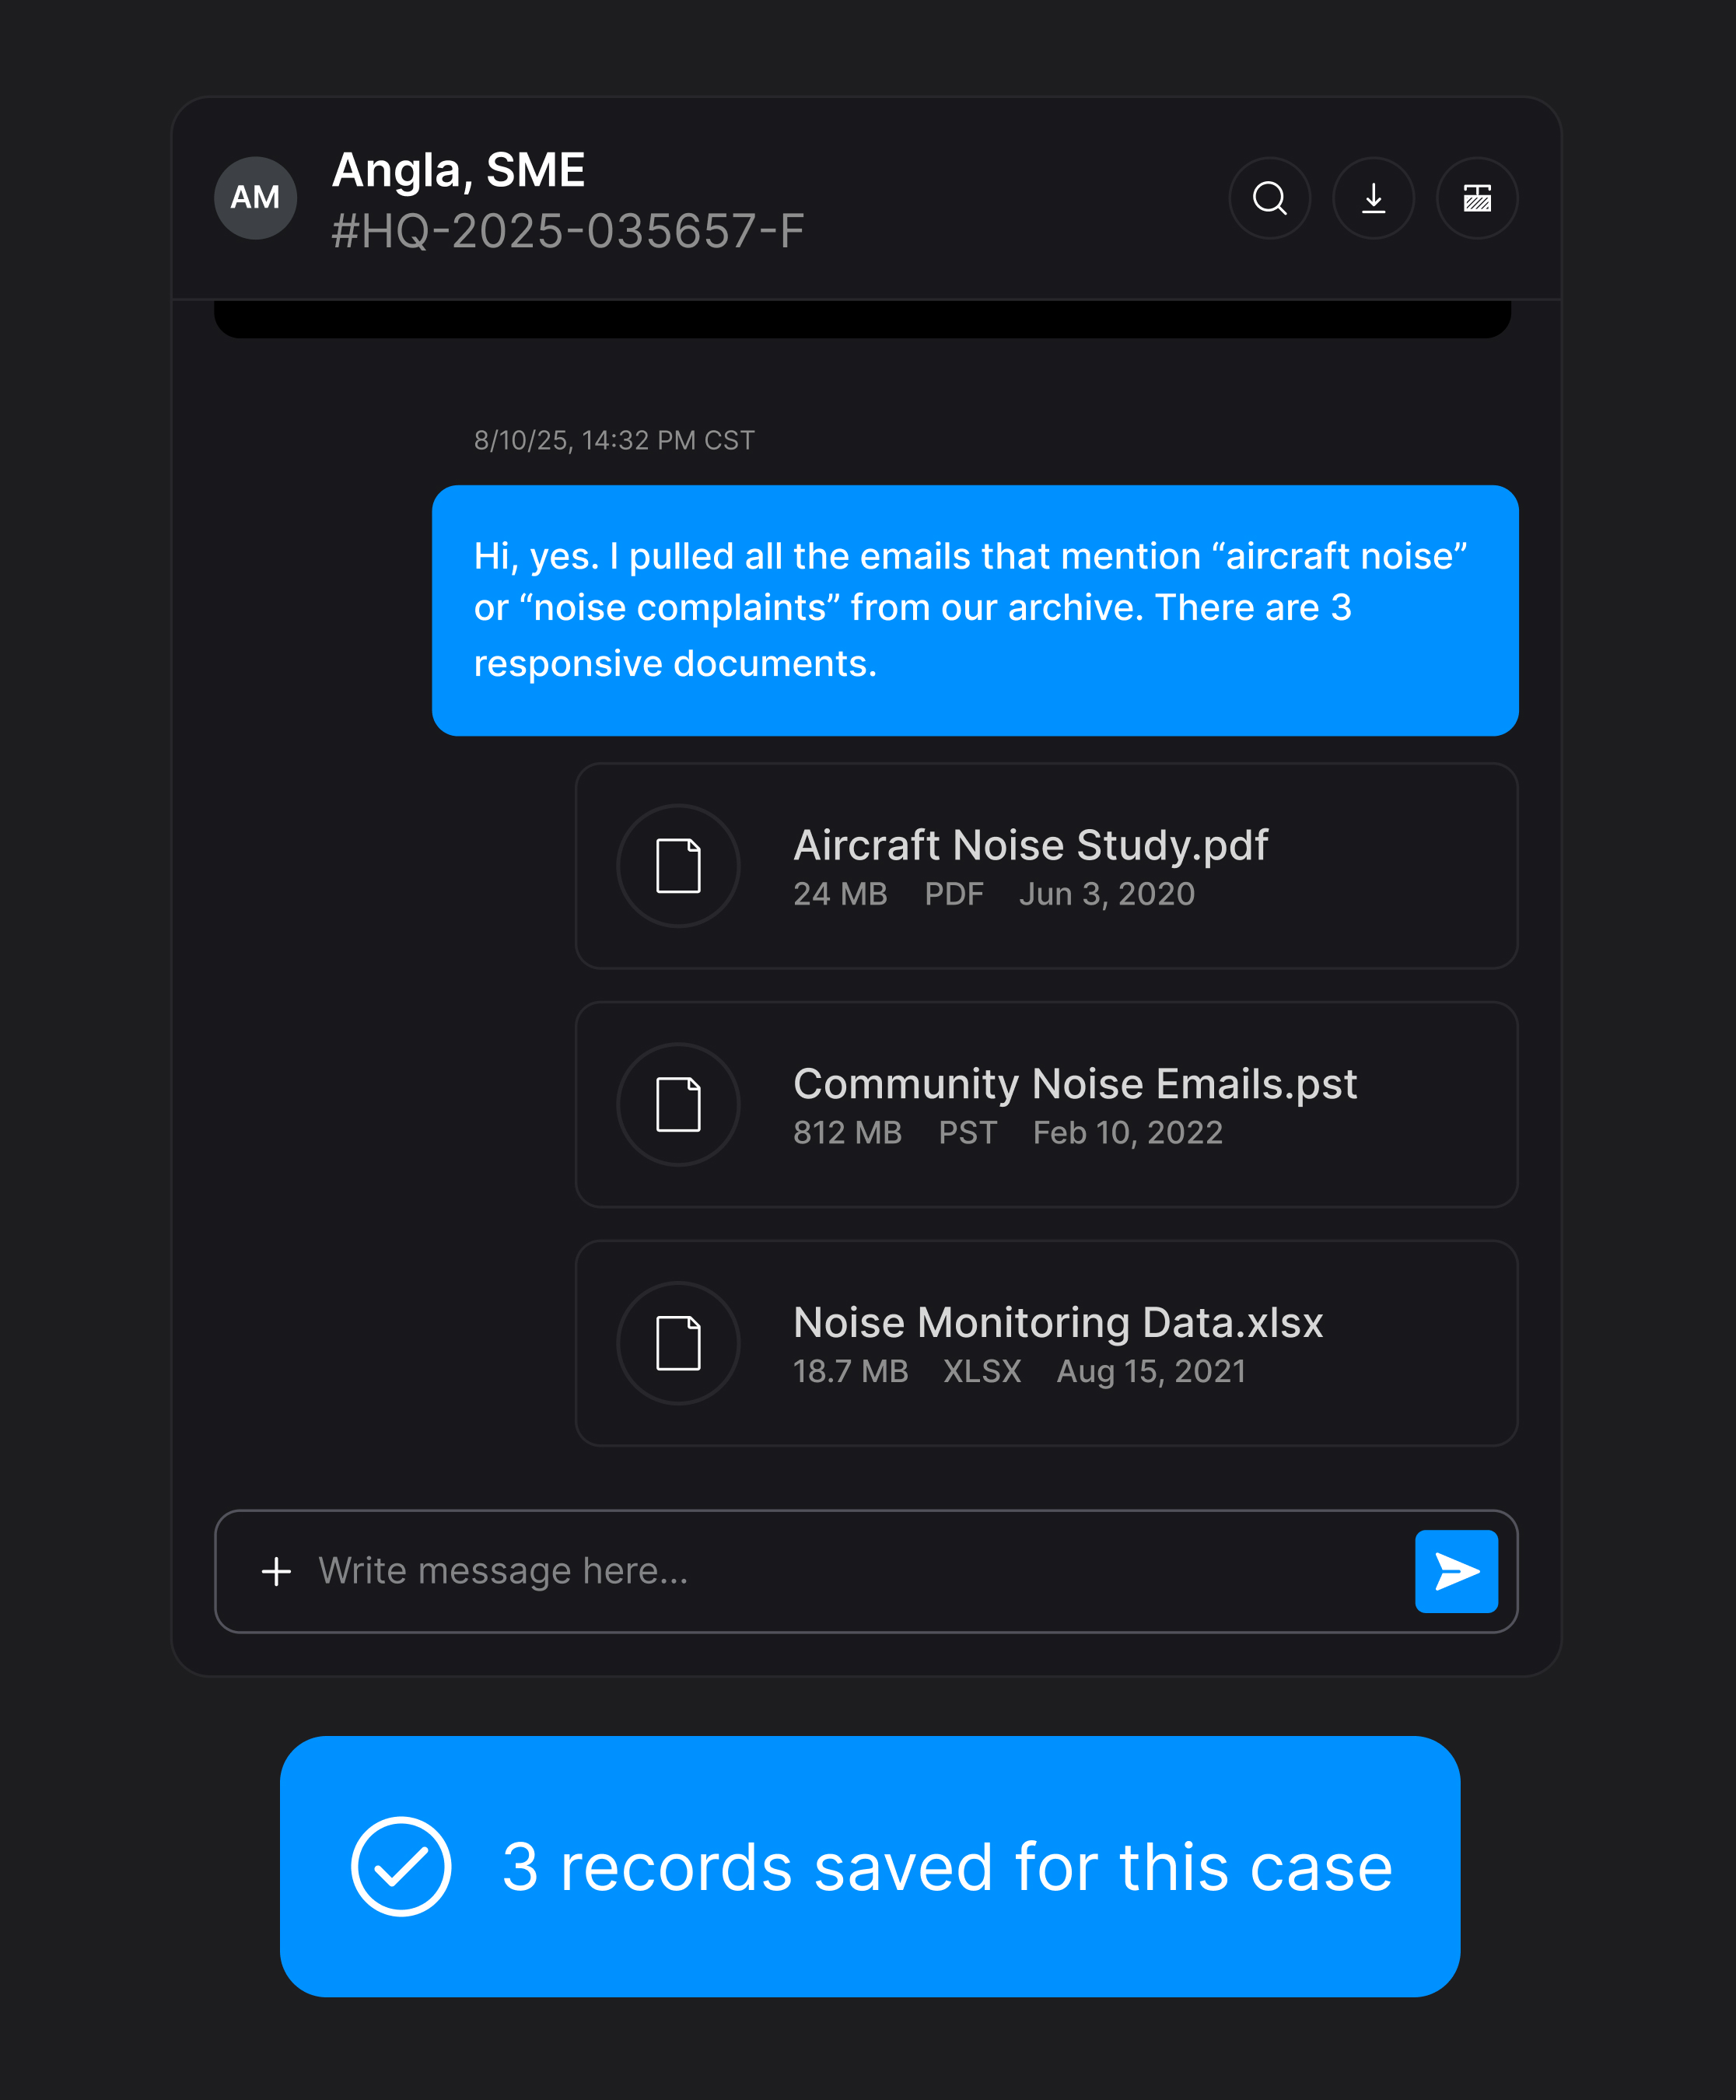
- Assess your current systems for risk, technical debt, and mission gaps
- Map a phased modernization path that keeps operations running
- Align architecture to Zero Trust, cATO, and CMMC requirements
- Plan data migration and integration with integrity verification
- Review sustainment, support, and certification options