Mission Applications Can't Afford Infrastructure Limitations
Applications that support active operations must perform under conditions that would break commercial systems — latency, interference, contested networks.
Legacy Applications Under Load
Aging platforms slow down exactly when operational tempo increases.
Point-in-Time Security Certification
Traditional ATO processes leave applications exposed between cycles.
No Resilience Under Adversarial Conditions
Applications designed for peacetime fail under active interference.
Modernization Requires Downtime
Upgrading applications that support active operations can't tolerate outages.
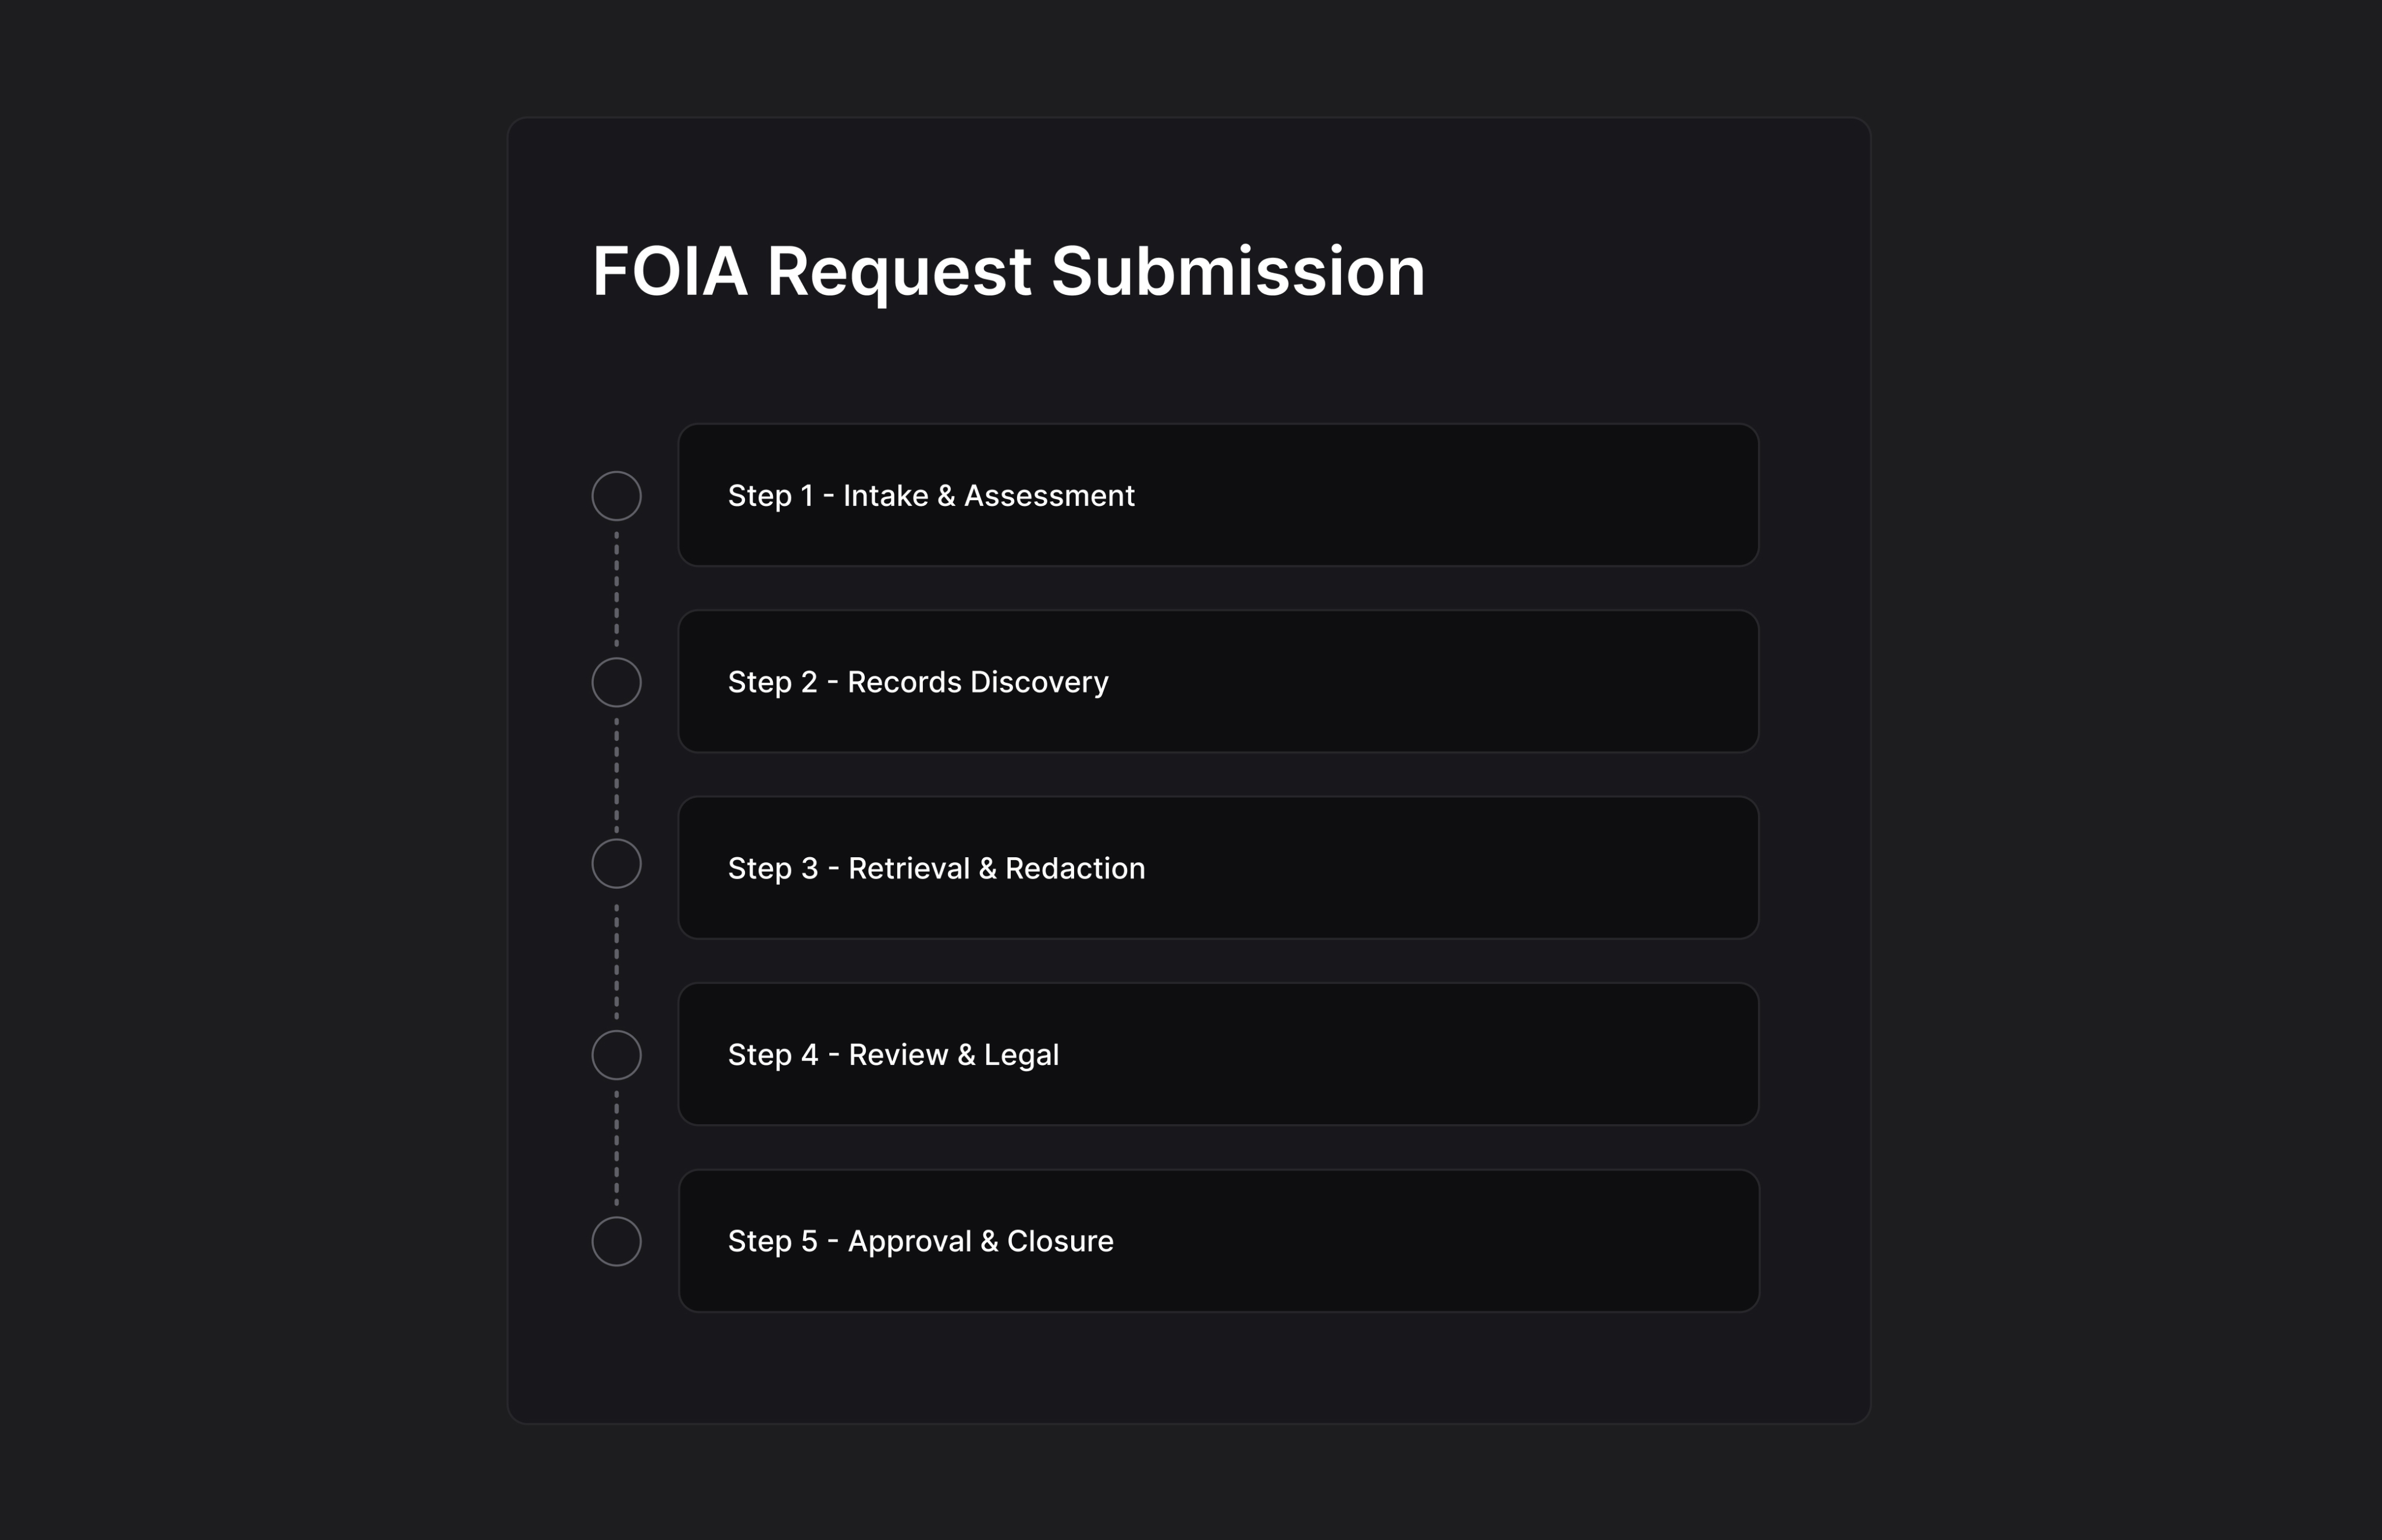
From requirements to sustained operations.
Mission Requirements
Mission Requirements
Define operational needs, constraints, and security mandates.
Security Architecture
Security Architecture
Design Zero Trust controls into the application from the start, not layered on after.
Application Engineering
Application Engineering
Build the application to perform under contested, high-tempo operational conditions.
Certification
Certification
Move through certification with continuous evidence collection instead of a one-time review.
Operational Deployment
Operational Deployment
Deploy into active operations with sustainment support from day one.

Mission Application Modernization
Upgrade aging applications without operational interruption.

Continuous ATO Architecture
Real-time compliance monitoring eliminates certification gaps.

Operational Resilience
Failover, degraded-mode ops, and recovery mechanisms built in.

Performance Engineering
Systems tuned for operational tempo, not commercial benchmarks.

Adversarial Hardening
Designed to perform under active interference and attack.

Zero-Downtime Deployment
Updates deployed without taking systems offline.
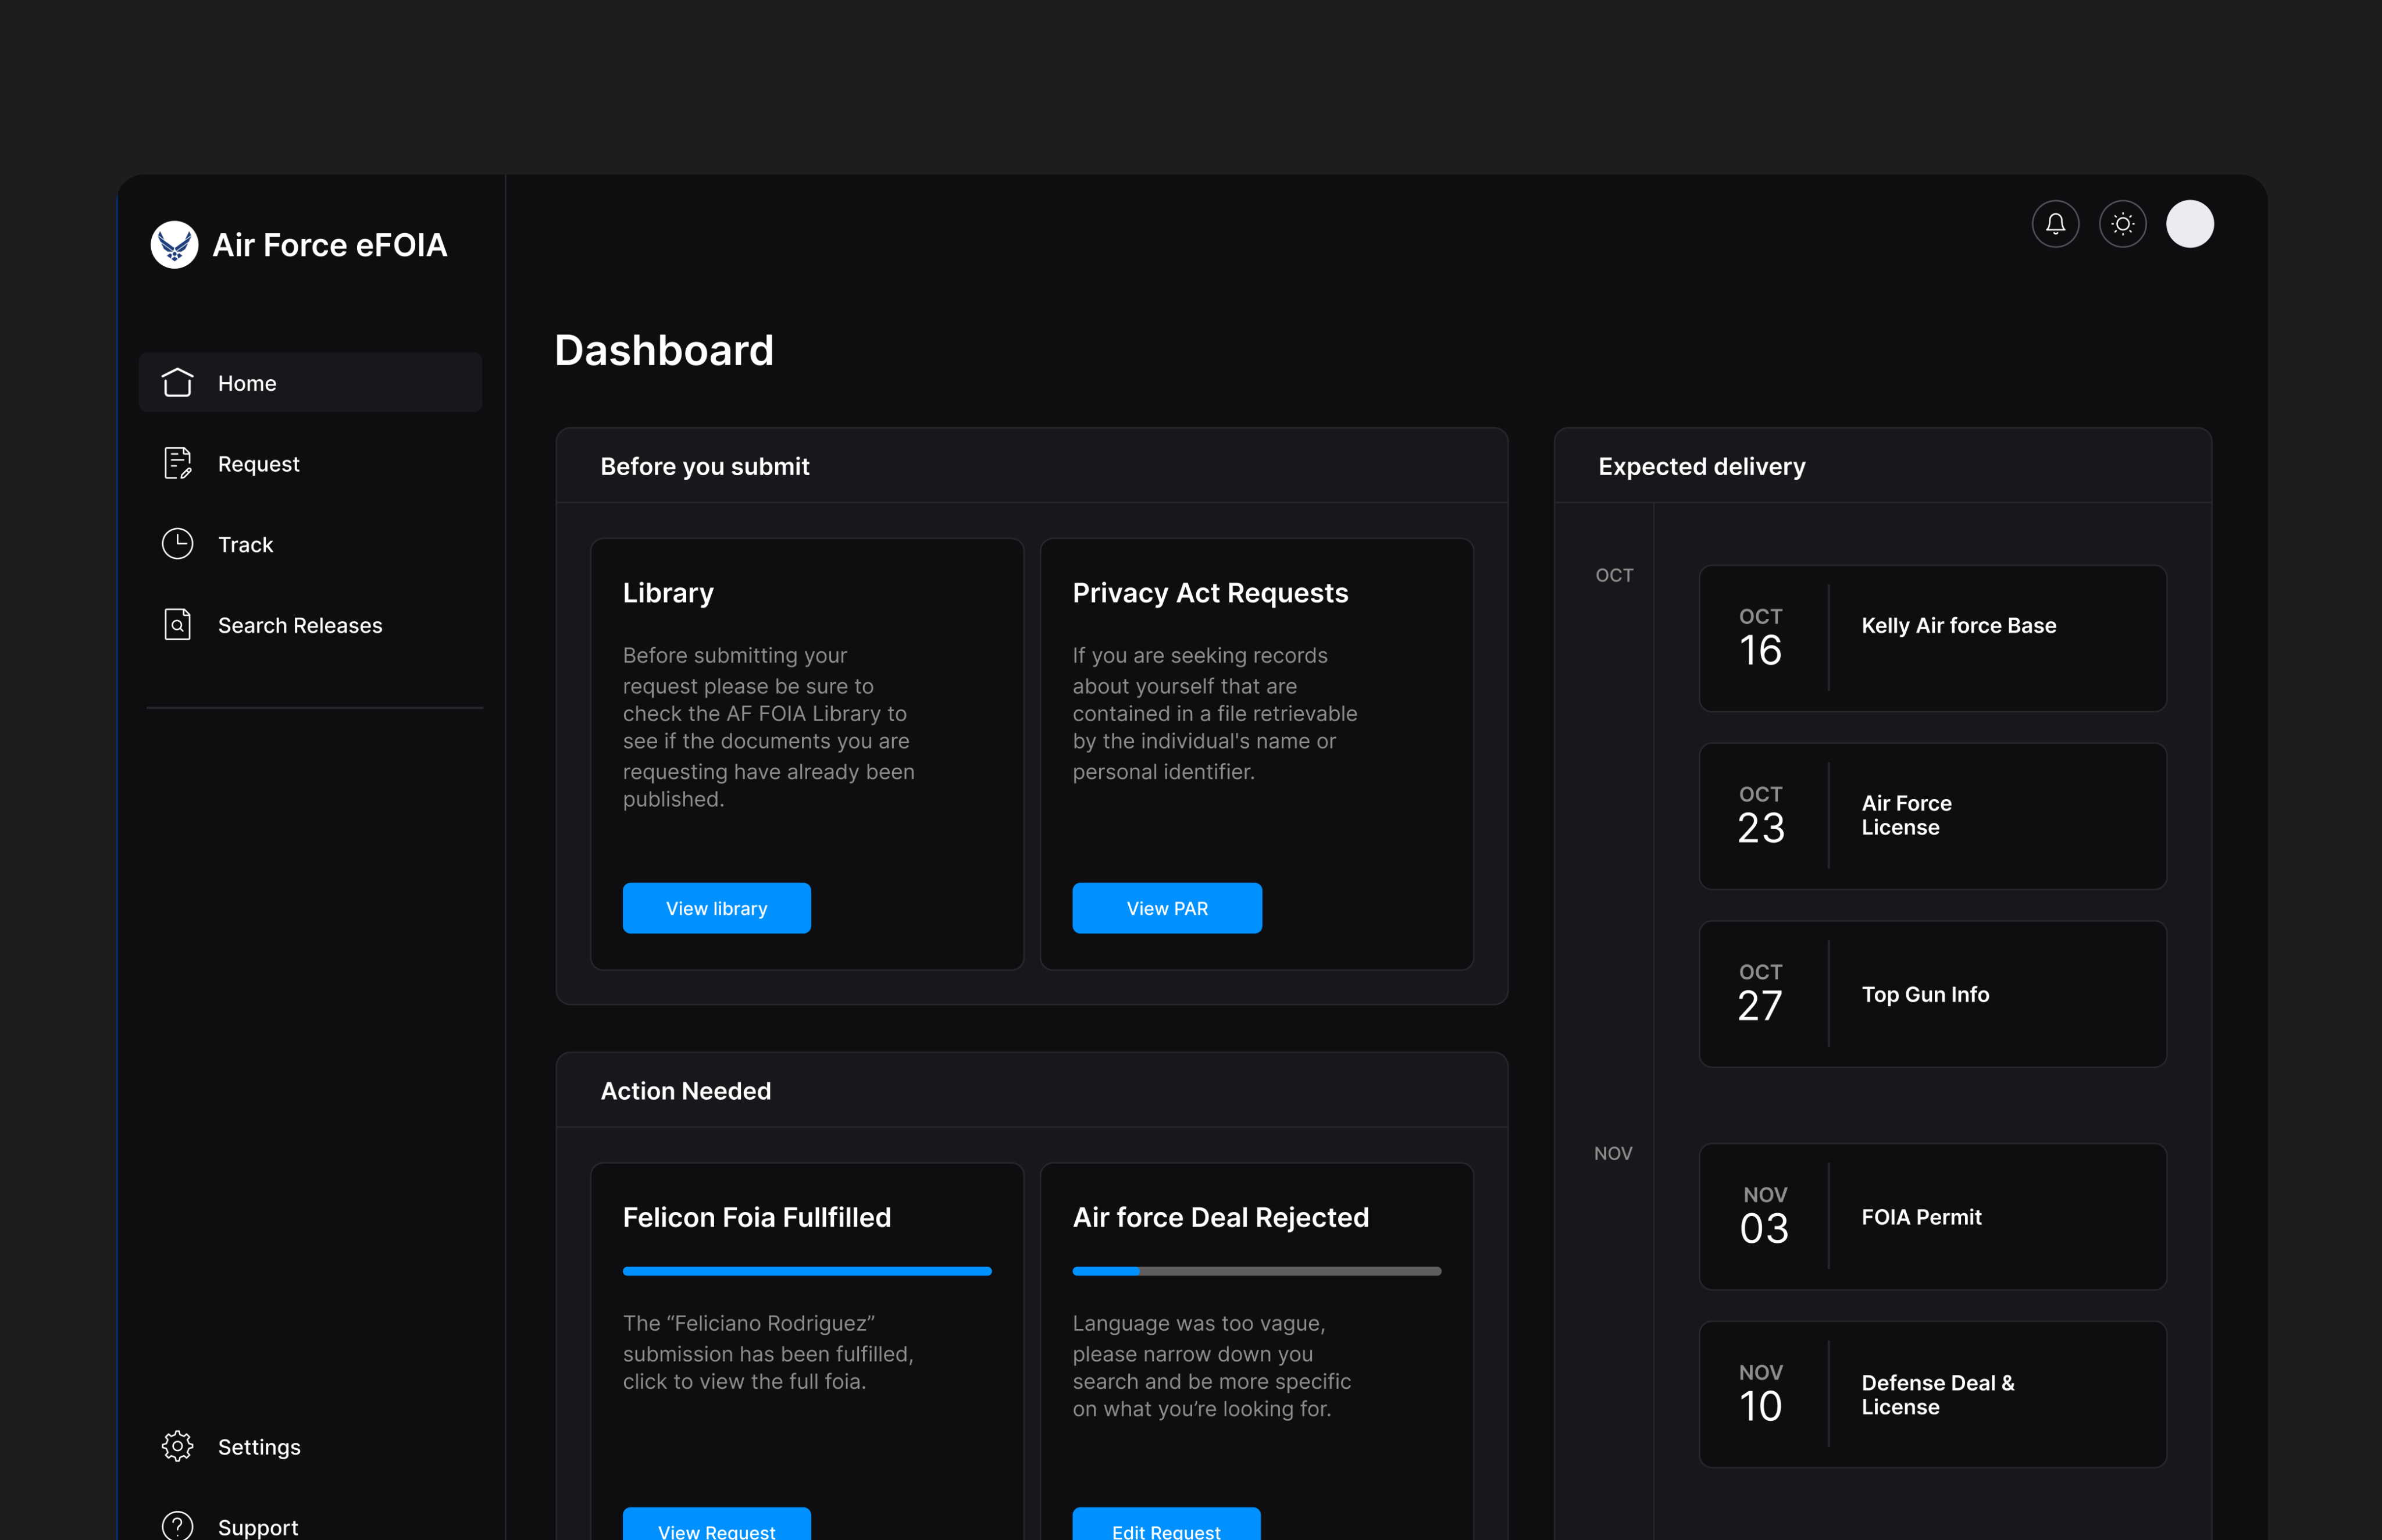
Continuous authorization
Continuous authority, zero gaps.
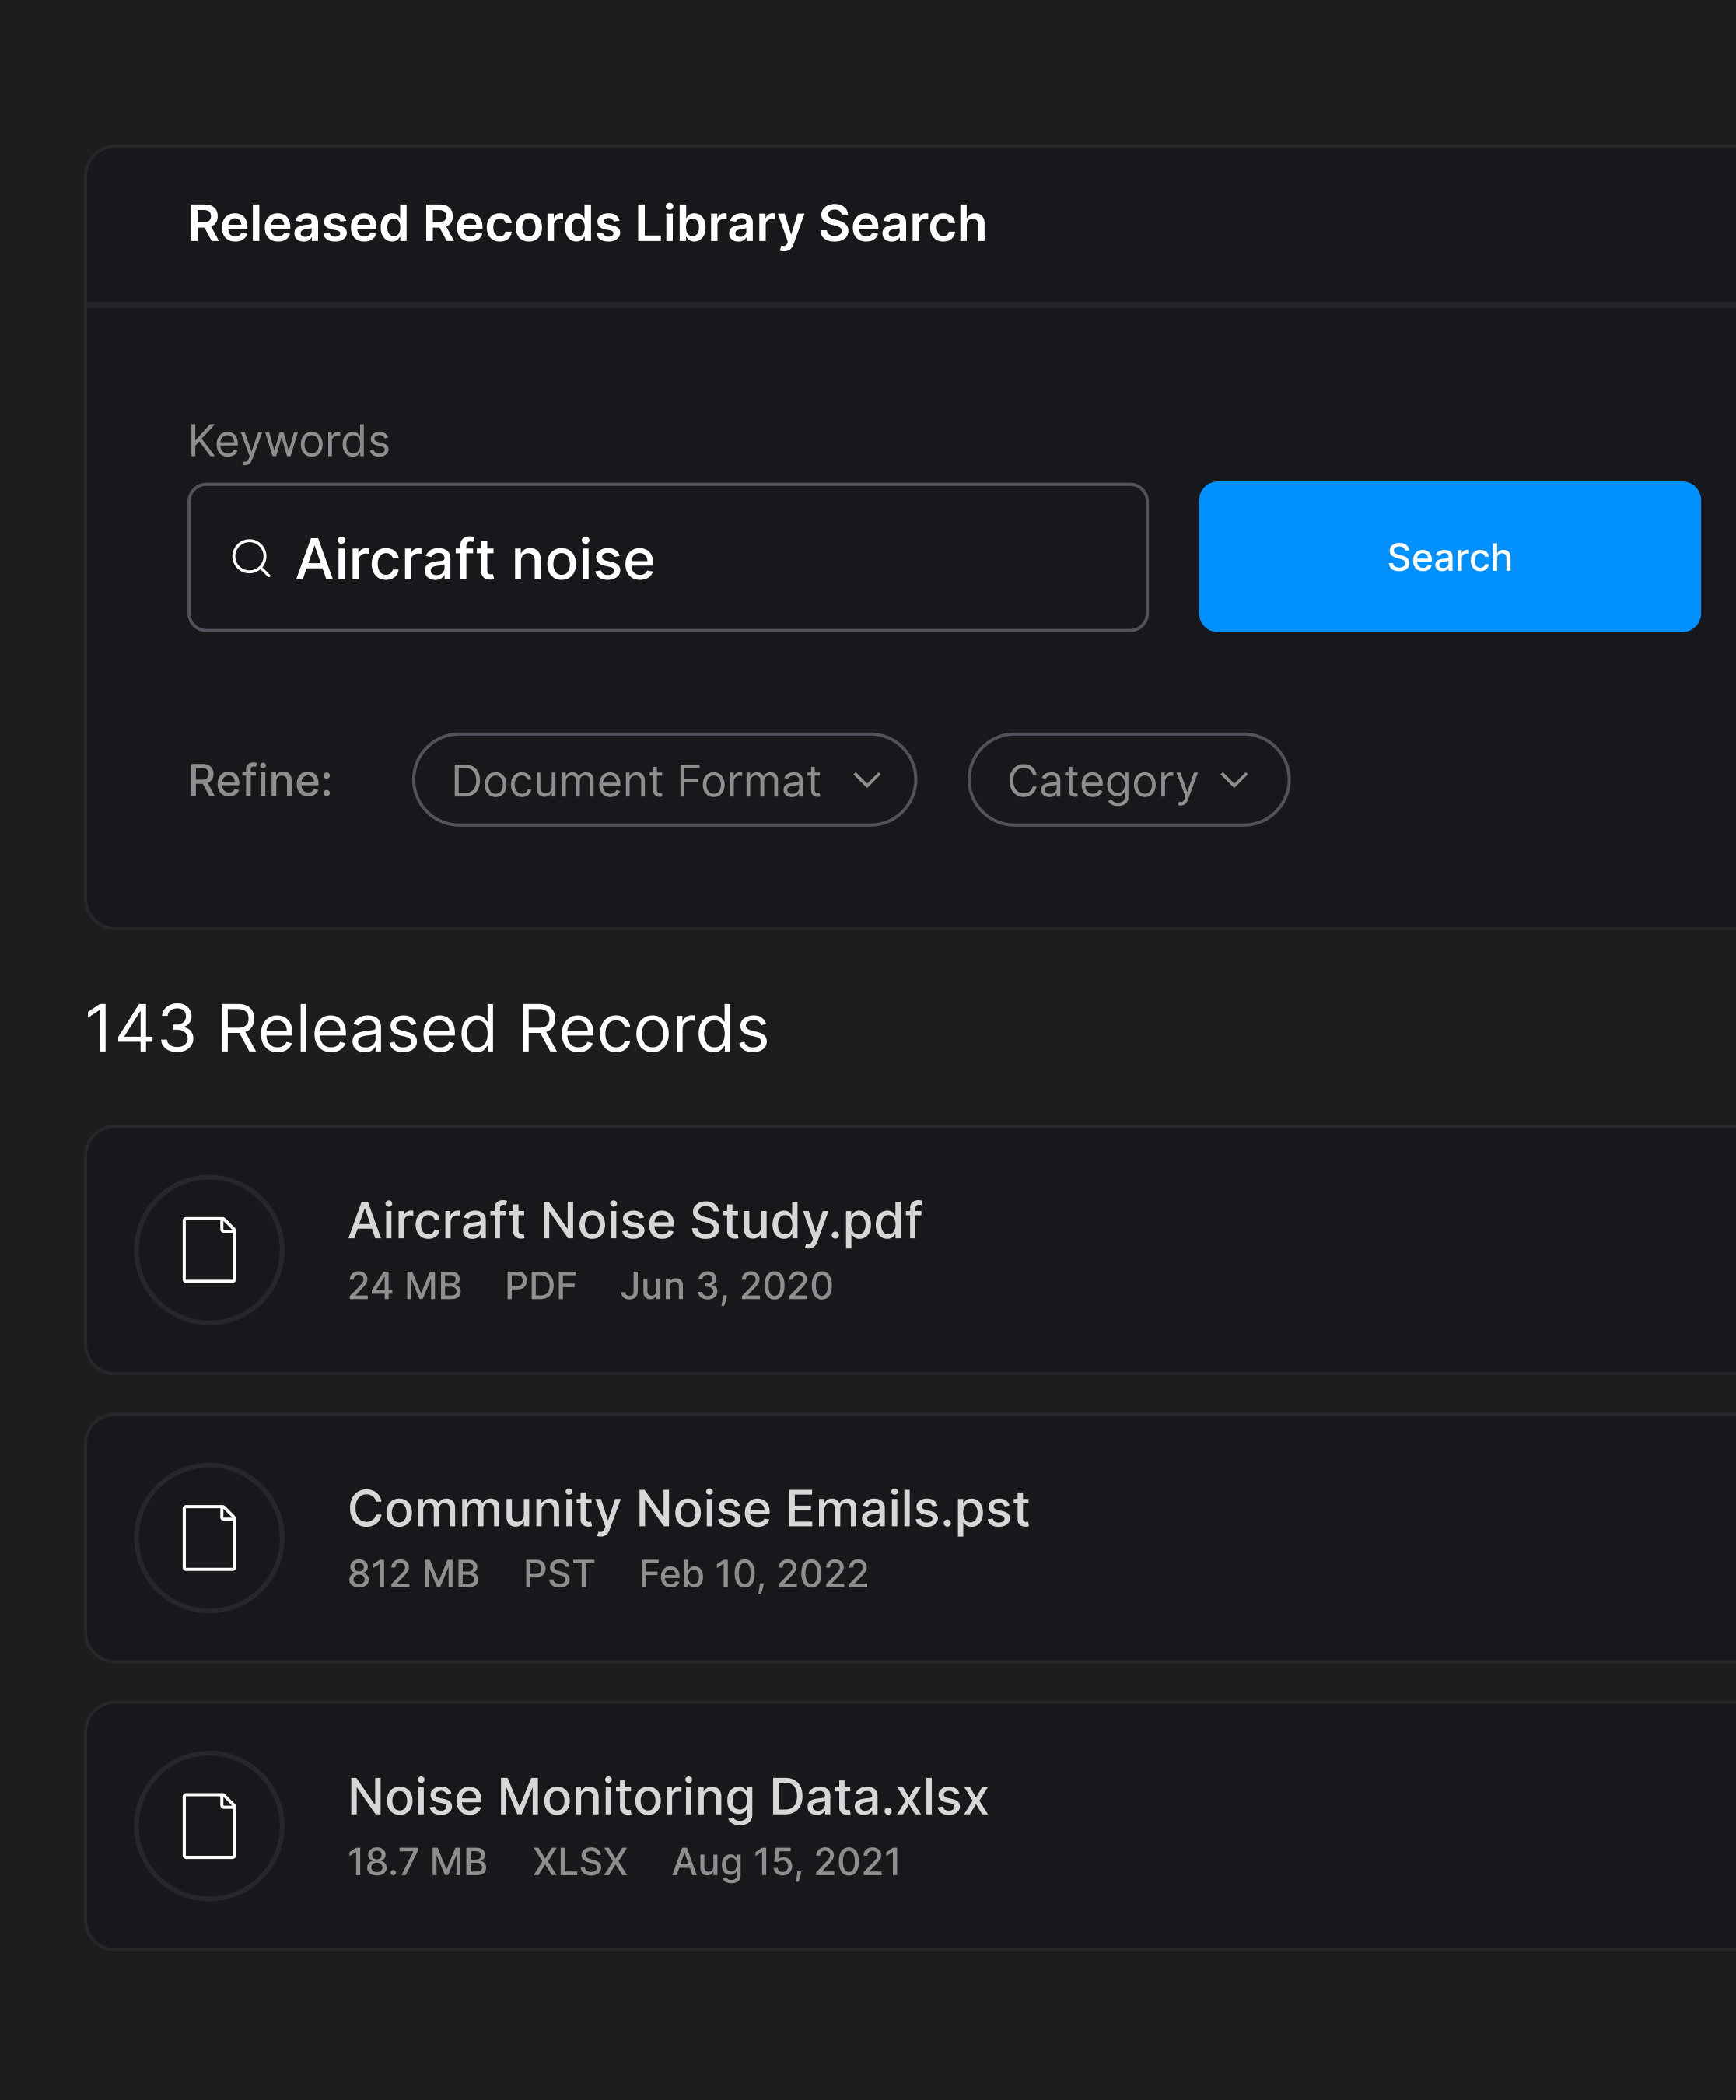
Continuous ATO model — real-time security monitoring, automated compliance checks, continuous authorization versus traditional point-in-time with exposed gaps.
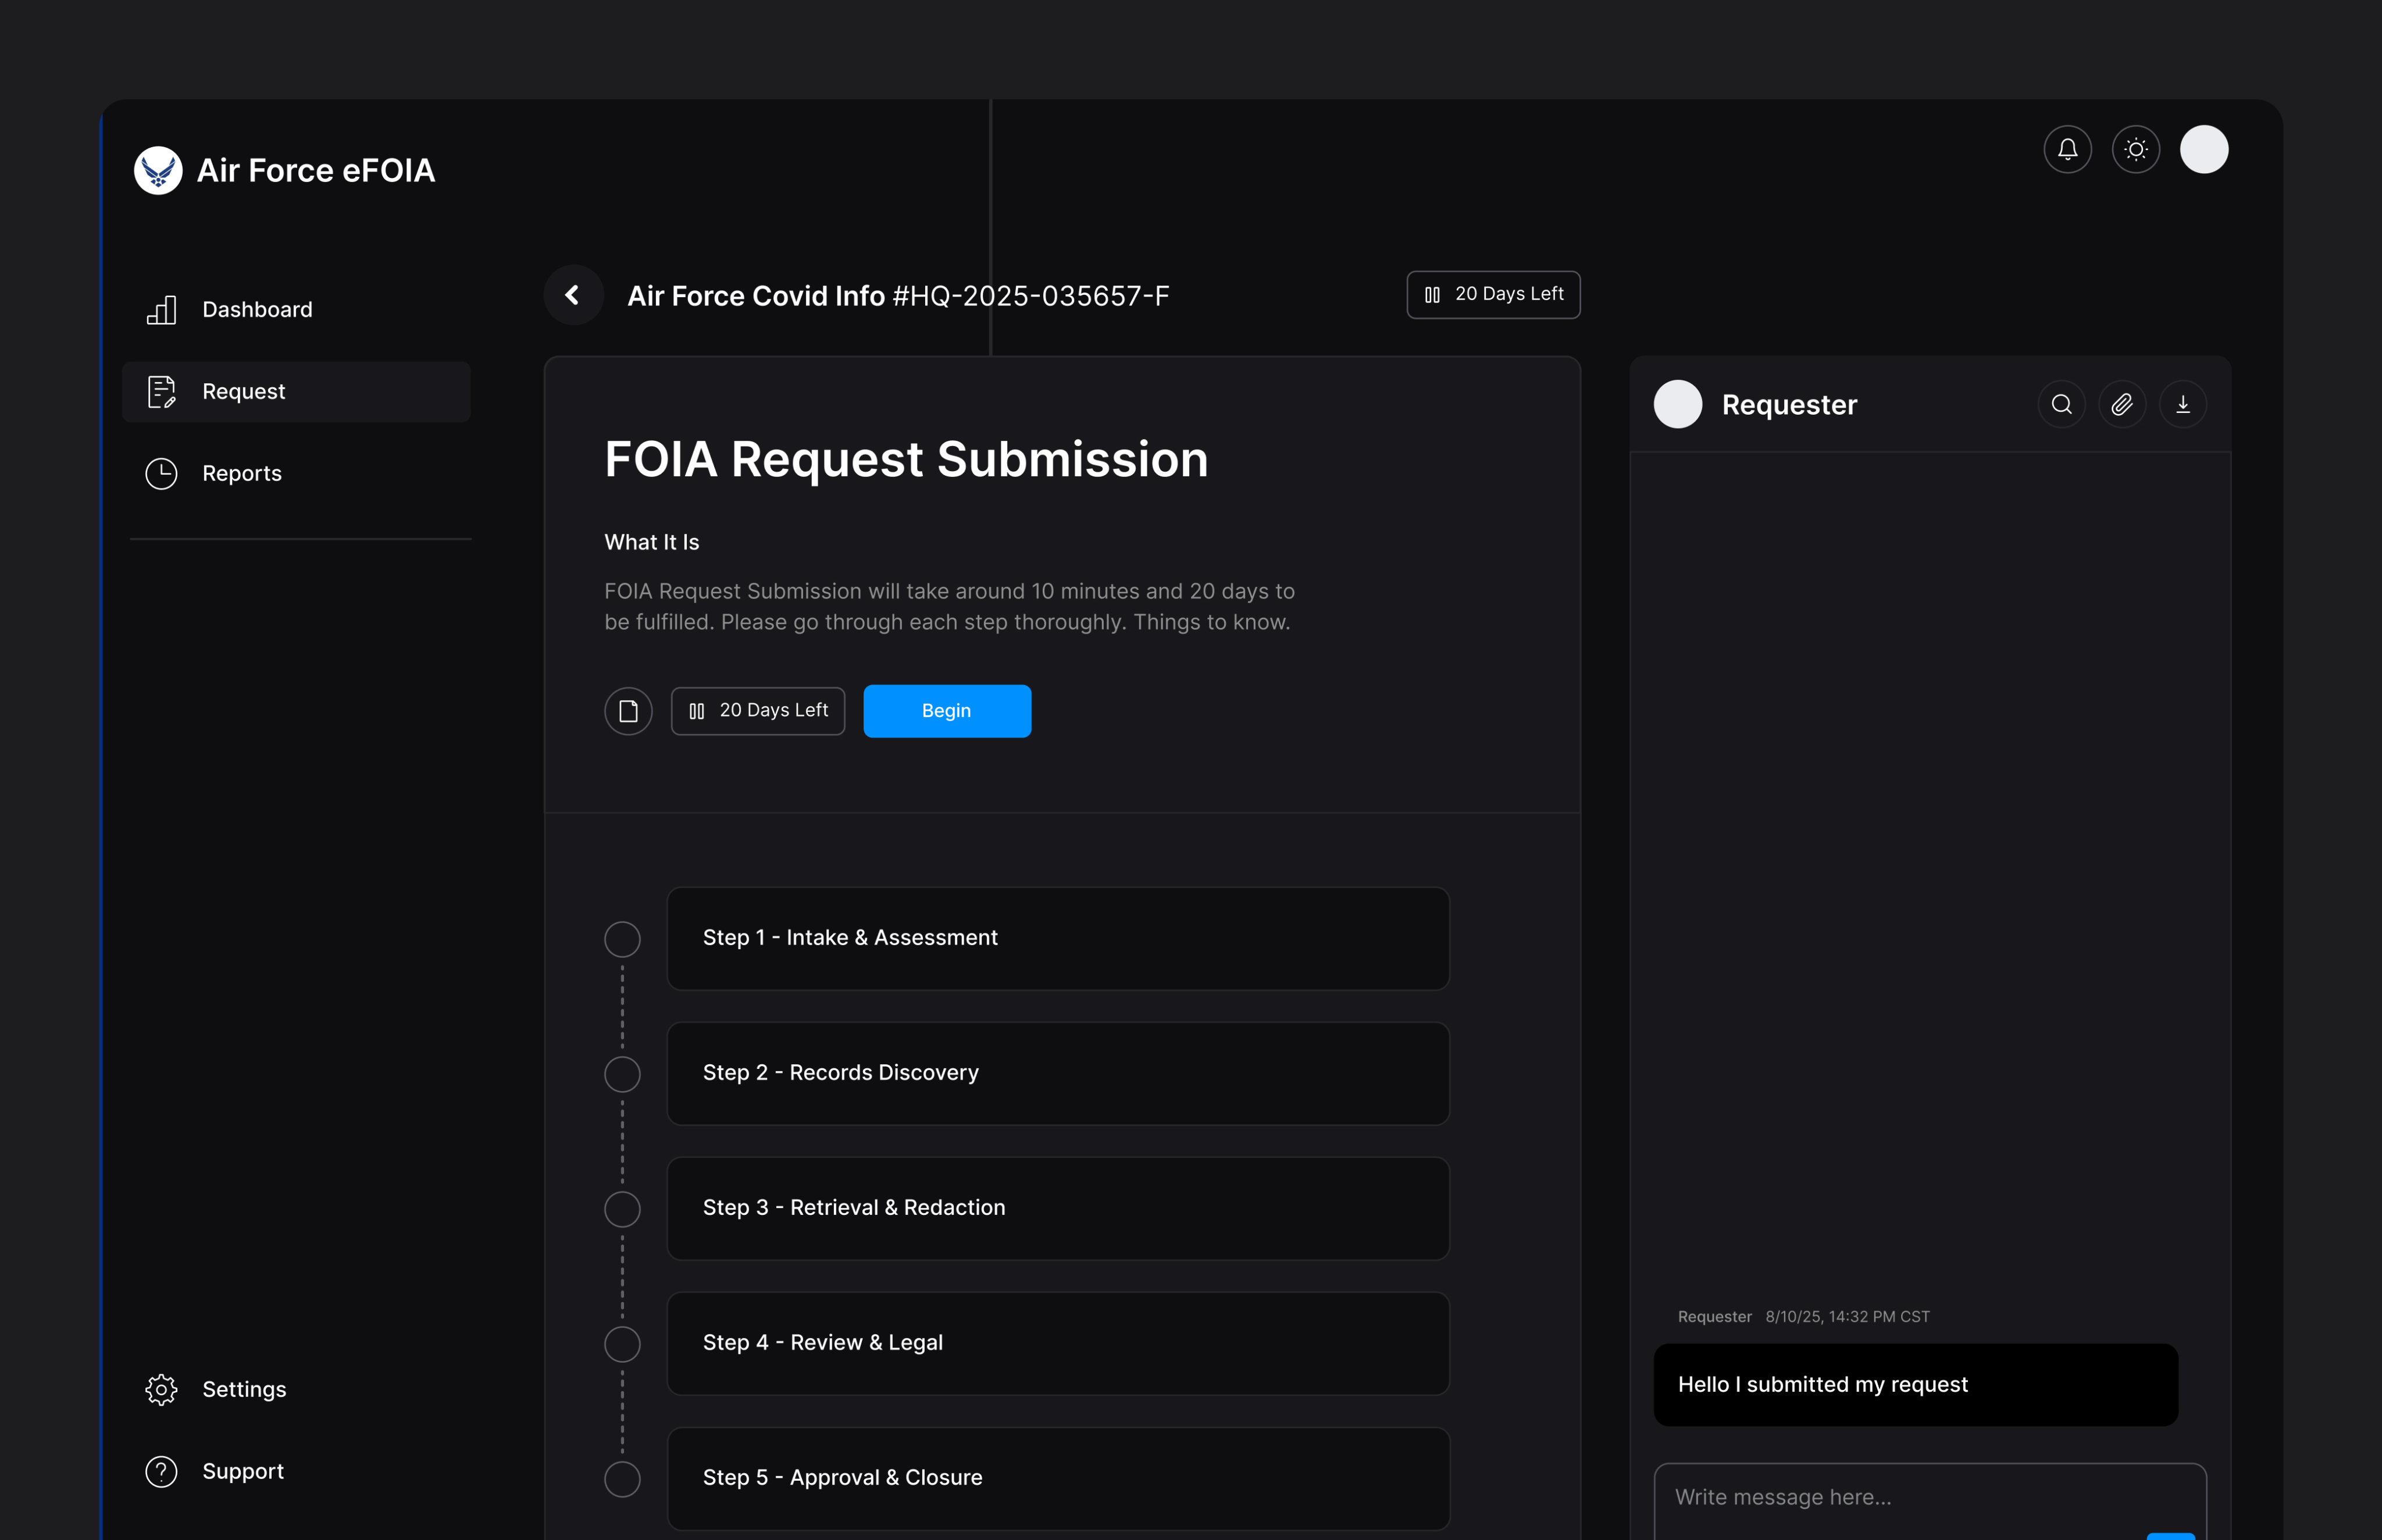
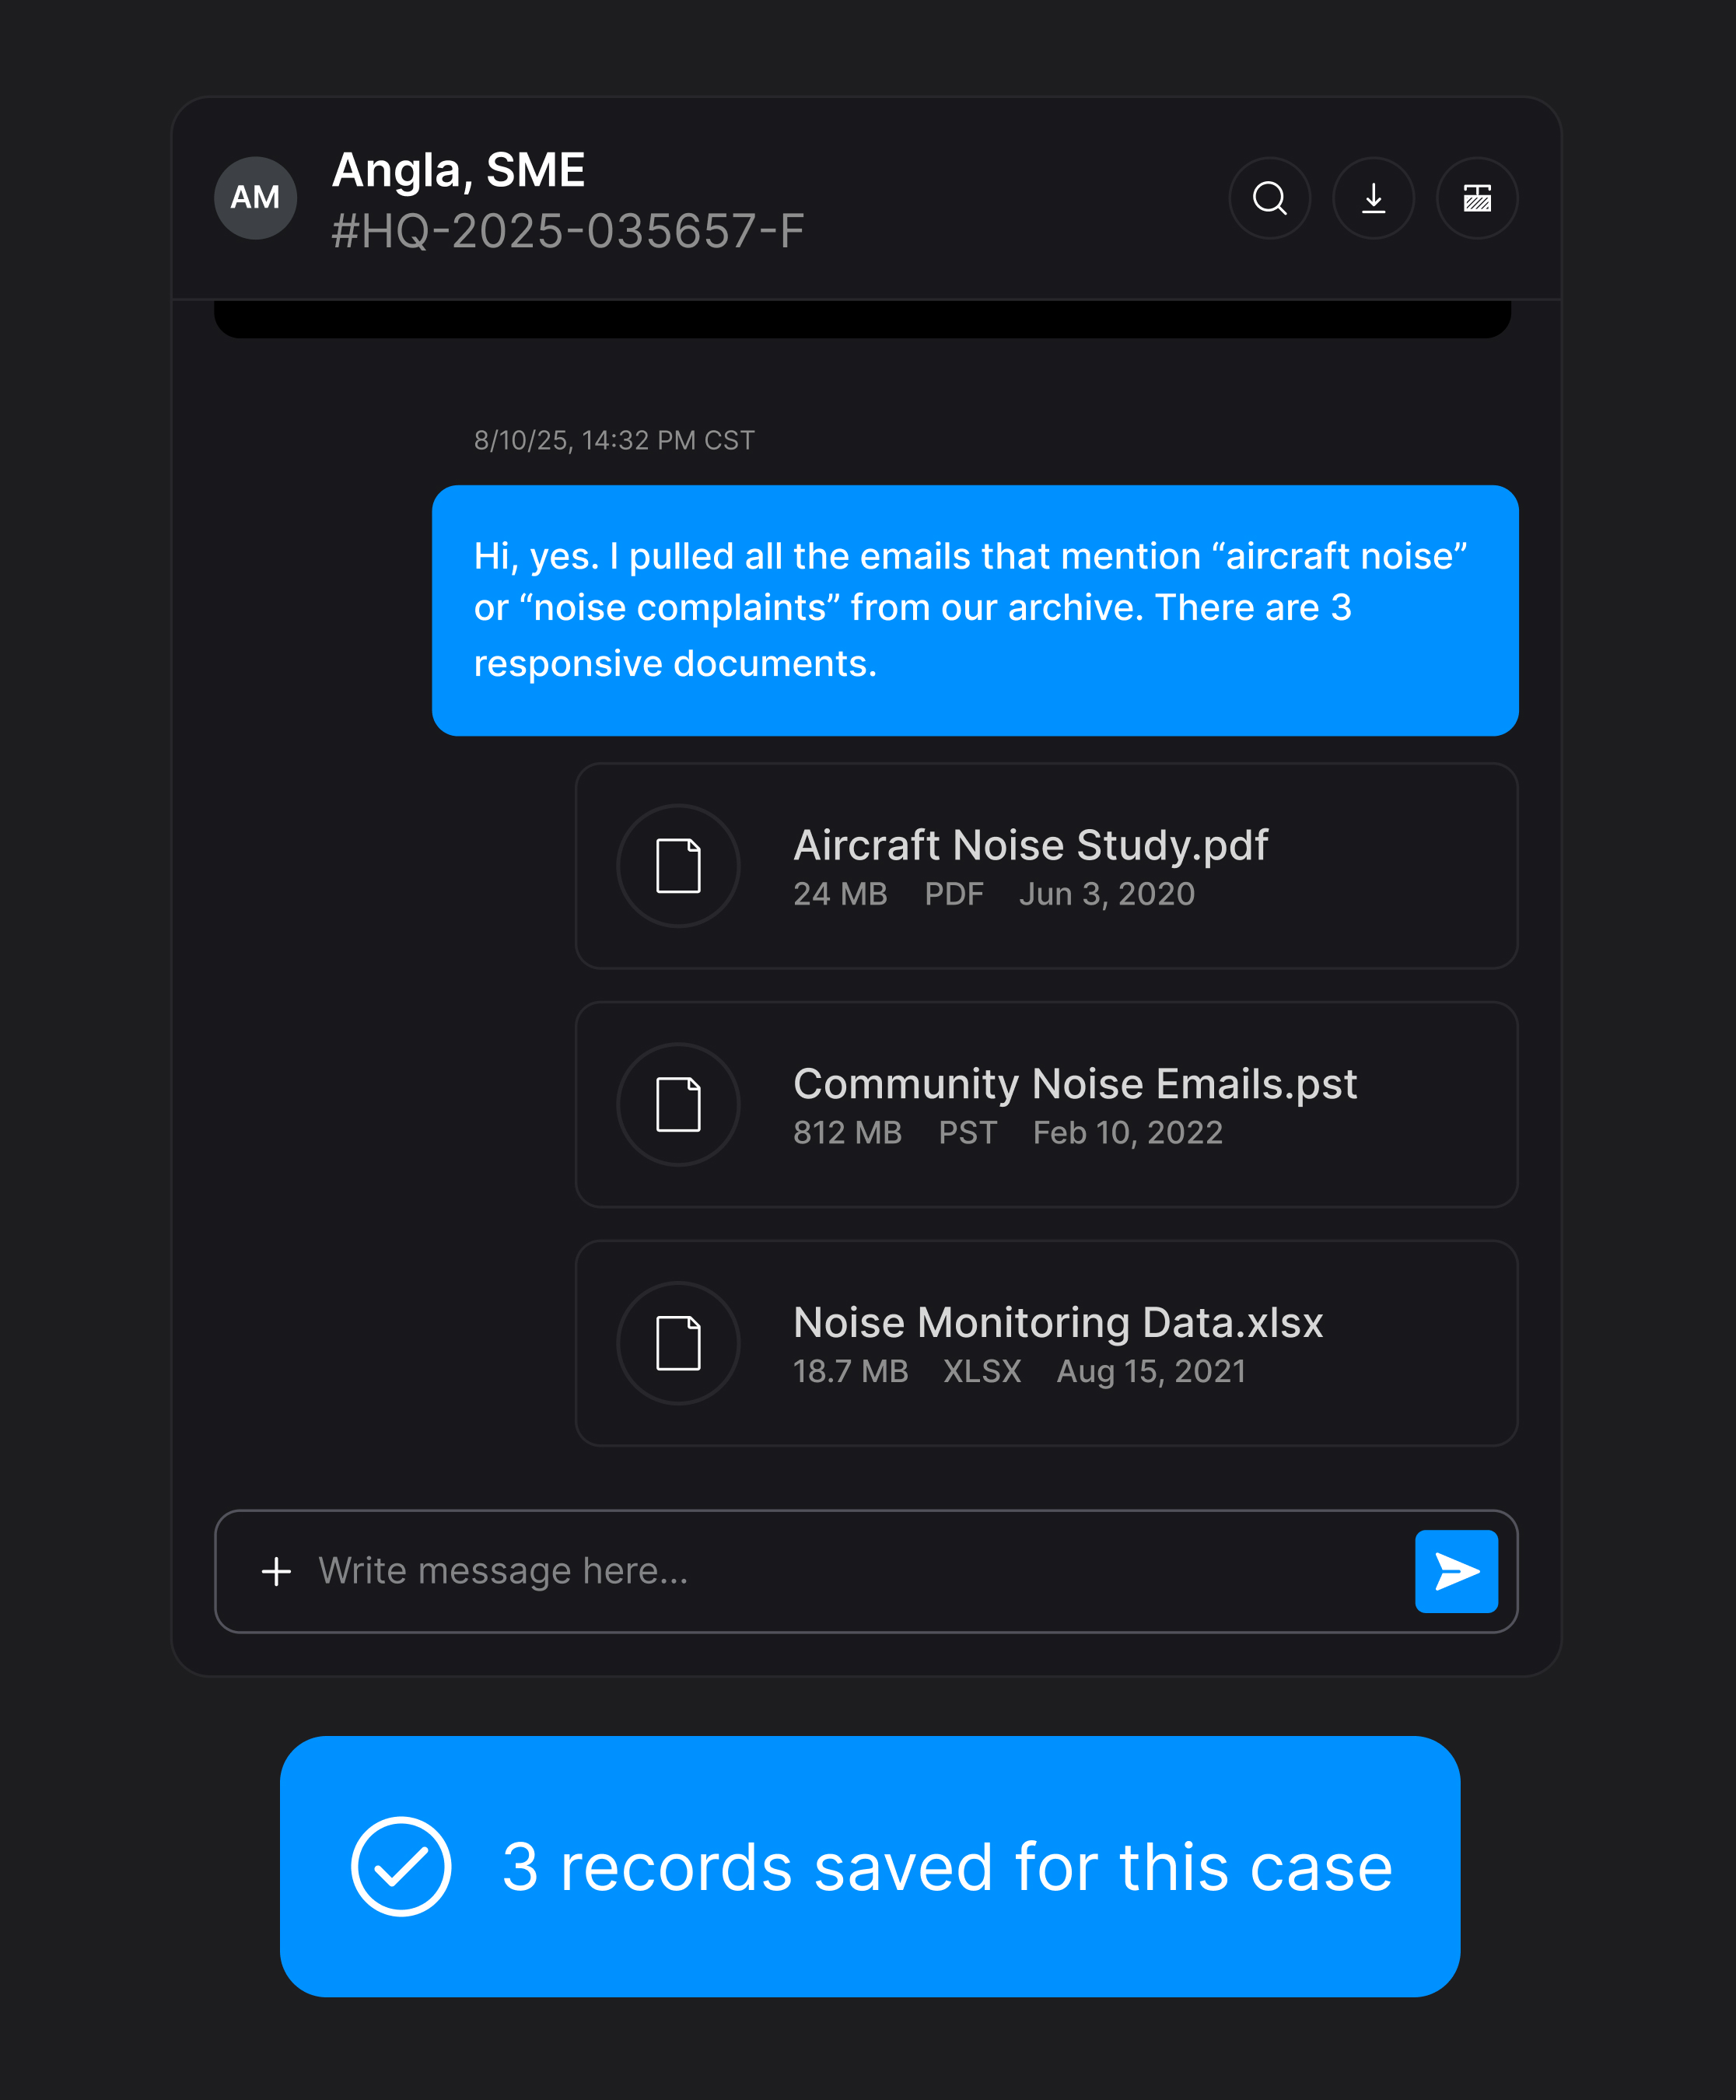
Operational resilience
Resilient under pressure.
Application resilience architecture — failover paths, degraded-mode operations, recovery mechanisms maintaining mission continuity during infrastructure stress.
Why Defense Agencies Choose DTSI
Proven with DISA and USAF. CMMI Level 3. CMMC Level 2. ICBM modernization experience.
Proven with DISA and USAF Commands
Delivered mission applications for AFLCMC, Air Mobility Command, DISA.
CMMI Level 3 + CMMC Level 2
Engineering maturity and cybersecurity certification for classified work.
ICBM Systems Modernization
Modernized the most mission-critical systems in the DoD inventory.
Customers + Partners
Trusted in IT & Cyber Expertise for 44 Years. We enable the DoD and all branches of service to maintain peak readiness and deliver mission results through proven technical expertise, operational support, and cybersecurity strength.
ARCADIS
City of San Antonio
State of Florida
State of New Jersey
Nantucket
United States Air Force
Copper River
Lockheed Martin
Booz Allen Hamilton
Abacus Technologies
Leidos
Northrop Grumman
ARCADIS
City of San Antonio
State of Florida
State of New Jersey
Nantucket
United States Air Force
Copper River
Lockheed Martin
Booz Allen Hamilton
Abacus Technologies
Leidos
Northrop Grumman
Book Your Personalized Demo
Discuss your mission application requirements with DTSI.
In your demo, we'll cover:
- Assess your current systems for risk, technical debt, and mission gaps
- Map a phased modernization path that keeps operations running
- Align architecture to Zero Trust, cATO, and CMMC requirements
- Plan data migration and integration with integrity verification
- Review sustainment, support, and certification options